Your Certificates Live on Your Domain, Not Ours
When recipients open a certificate, they see your organization’s name in the URL. Not mixcertificate.com. Your brand front and center, from the first click to the verification page.
Why It Matters
The URL your recipients see is part of your brand
When a recipient opens their certificate and sees mixcertificate.com in the browser, they are looking at someone else’s name. When they see certificates.yourorganization.com, the credential belongs to you. That difference matters every time someone shares or verifies a certificate.
- Recipients trust links from a domain they recognize
- Certificates look like they come from your organization, not a third-party tool
- Your domain appears on every share, every email, every QR scan
- No "Powered by MixCertificate" text visible to recipients
- Consistent brand experience from email to certificate to verification page
Brand Trust
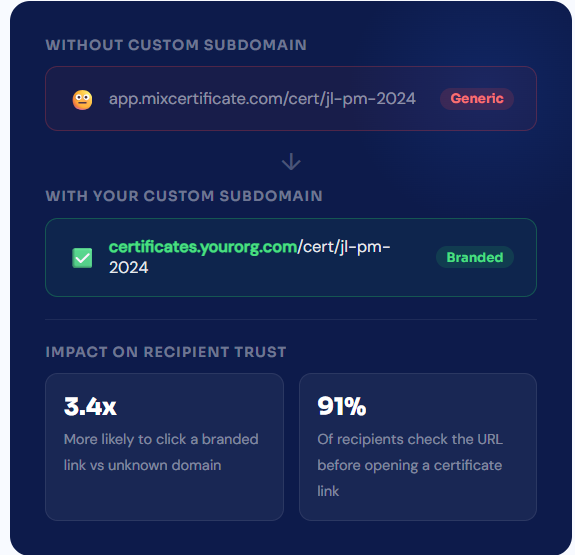
What recipients experience before and after
The difference is not just cosmetic. A branded URL changes how recipients perceive the credential itself.
- Without Custom Subdomain
Looks like a tool, not a credential
Recipients land on a generic platform page. The URL, header, and footer all say MixCertificate. Your organization’s name appears somewhere in the middle. It feels like a template, not an official document.
- URL shows a third-party platform name
- Recipients may question if the certificate is real
- Platform branding competes with your organization's identity
- Sharing the link promotes the platform, not your brand
- Feels like a free tool rather than a professional system
- With Your Custom Subdomain
Looks official. Feels professional.
Recipients see your domain in the browser the moment they click the link. The page carries your logo, your name, your design. The certificate feels like it came from an organization with real infrastructure.
- URL instantly recognizable as coming from your organization
- Trust established before the page even finishes loading
- Your brand is all recipients see, start to finish
- Every share and link click reinforces your organization's name
- Credential looks like it belongs to a serious organization
Everything that comes with your custom subdomain
Not just a URL change. Your subdomain becomes a full branded certificate portal with all the features you already use.
Free SSL Certificate
Every custom subdomain gets a free SSL certificate provisioned automatically. Recipients see the green padlock and HTTPS without you lifting a finger.
Fully White-Labeled
No MixCertificate logo, footer, or branding appears anywhere on the certificate pages. Recipients only see your name, your logo, and your colors.
Retroactive for All Certificates
Set up your subdomain once and every certificate you have ever issued through MixCertificate immediately moves to the new URL. Nothing expires or breaks.
Works With Any Registrar
GoDaddy, Namecheap, Cloudflare, Google Domains, Route 53, or anywhere else you manage your DNS. The setup process is the same: one CNAME record.
Custom Verification Pages
The verification page recipients land on after scanning a QR code also lives on your subdomain. Your brand through the entire verification journey.
Global CDN Delivery
Certificates load fast everywhere in the world because your subdomain routes through MixCertificate's global CDN. No extra setup required.
Easy Process
Certificate Hosting: Automatic & Effortless
From generation to permanent hosting in milliseconds
Step 1: Generate Certificates
Create certificates through our platform using bulk upload, templates, or API integration. Design once, generate thousands.
Step 2: Automatic Cloud Upload
The moment a certificate is generated, it’s automatically uploaded to secure, redundant cloud storage across multiple geographic regions.
Step 3: Unique URL Assignment
Each certificate receives a permanent, unique URL on your custom domain: yourschool.edu/cert/[UNIQUE-ID]
Step 4: Global Distribution
Certificate URLs become accessible worldwide through our global CDN. Available from 200+ edge locations for fast loading anywhere.
Step 5: Permanent Hosting
Certificates remain hosted permanently with 99.9% uptime guarantee. No expiration dates. No renewal fees. Hosted forever.
Technical Setup
One DNS record. Five minutes. Done.
You do not need a developer to set this up. If you can log in to your domain registrar, you can add a CNAME record. MixCertificate detects it automatically and does the rest without any back and forth.
- Works with GoDaddy, Cloudflare, Namecheap, Google Domains, Route 53, and more
- MixCertificate detects the record and provisions SSL without manual steps
- Zero downtime migration: existing certificate links stay working during the switch
- Step-by-step setup guide available for every major registrar inside the dashboard
- Support team available if anything does not propagate as expected
Multi-Organization
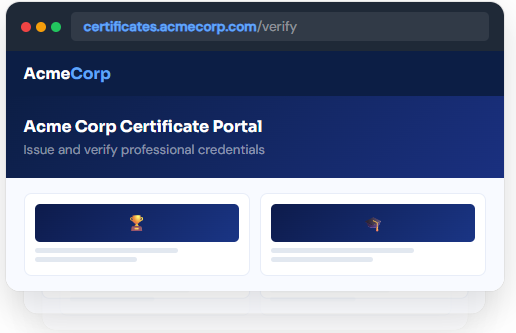
Every organization gets its own subdomain, fully separate
If you manage certificates for multiple clients, departments, or brands, each one can have its own subdomain pointing to its own certificate portal. Everything is isolated and branded independently.
Put your brand on every certificate you issue
Five minutes to set up. Free on every plan. No developer required.
#Custom Subdomain
Questions people usually ask first
Frequently Asked Questions
No. The old links redirect automatically to the new subdomain URL. Recipients who already have a certificate link will land on the right page. Nothing breaks during or after the migration.
No. We handle 100% of hosting infrastructure servers, CDN, SSL certificates, backups, security updates, scaling. You never touch technical infrastructure.
We support files up to 50MB per certificate. Our CDN optimizes delivery for fast loading even with large files. We r
Yes. Certificates can be hosted on your custom domain or subdomain: certificates.yourschool.edu or credentials.yourcompany.com. We handle all DNS and SSL certificate configuration.
Yes. You can register a domain specifically for certificates if you want to keep it completely separate from your main website. Any domain you control works.
Our multi-region architecture ensures certificates remain accessible even if one AWS region goes down. Automatic failover to backup regions maintains 99.9% uptime guarantee.
Yes. You can set certificates to require authentication before viewing. Perfect for internal documents or sensitive credentials that shouldn’t be public.
Recipients simply click the URL in their email or type it into any browser. No app downloads, no account creation, no login required. Works on any device instantly.